

JFrog Partners and Atlassian: a secure software supply chain, faster delivery
JFrog Software Supply Chain Security and universal artefact management act as the link between build and deployment, seamlessly integrated into your Atlassian platform.
What is JFrog Software Supply Chain Security?
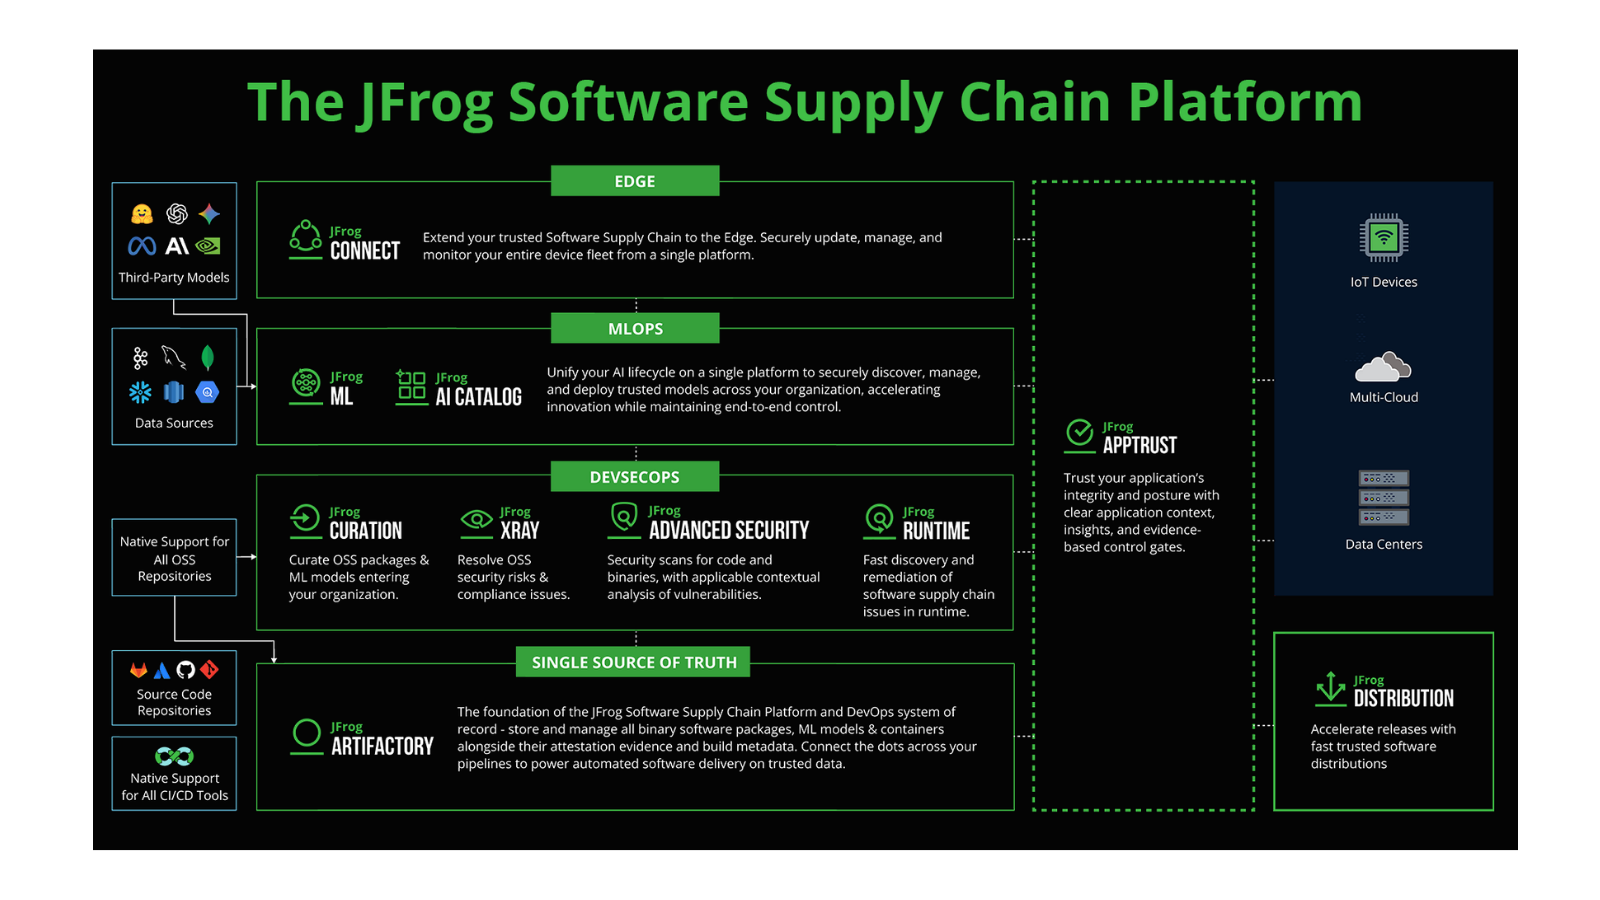
The JFrog platform at a glance
Artifactory

A universal repository for packages, containers and build artefacts: the central foundation for reproducible releases.
X-ray

Analysis of artefacts and dependencies to identify vulnerabilities, licence risks and compliance breaches.
Curation

Open-source package curation: High-risk or malicious packages are detected and blocked before they are downloaded.
Advanced Security

Advanced analyses such as secrets scanning, malware detection and context-based security assessments.
AppTrust

Governance, release and compliance rules for controlled and traceable software releases.
Distribution

Secure distribution of binary artefacts and release bundles to remote sites and environments.
ML & AI Catalogue

Backup, indexing and management of AI and machine learning models and components.
Runtime

Real-time monitoring of applications within the runtime environment and greater transparency regarding risks.
Connect

Remote updates and centralised management of edge and IoT devices.
JFrog Partner & Atlassian: Secure Software Delivery in Action
The integration of JFrog into the Atlassian platform closes a critical gap in the DevOps lifecycle: the link between code, build and deployment.
Where JFrog fits into your DevOps toolchain
Typical use cases

Scenario 1: Enterprise CI/CD with multi-technology stacks
Several teams work with different technologies such as Java, Node.js, Python and Go. JFrog Artifactory serves as a central repository for all formats, including npm, Maven, PyPI, Go and Docker, with standardised access rights and retention policies. Jira provides the planning layer, whilst Bitbucket or GitLab handle the pipelines. This creates a scalable JFrog software supply chain for secure software delivery.

Scenario 2: Container-based deployments
Docker images and Helm charts are version-controlled in Artifactory, scanned for vulnerabilities, malware and secrets using JFrog Xray and Advanced Security, and deployed to Kubernetes clusters via promotion workflows. Jira tracks the entire process from feature request to deployment.

Scenario 3: Software Supply Chain Security (SBOM)
Regulatory requirements, such as the EU Cyber Resilience Act, call for traceable software supply chains. JFrog generates automated Software Bills of Materials (SBOMs) for all artefacts. Curation protects against risky open-source dependencies, whilst compliance status is visualised in Jira dashboards.

Scenario 4: Hybrid and multi-cloud deployment
Artifacts must be available across different regions and cloud environments. JFrog Distribution and Replication synchronise and distribute repositories via AWS, StackIT or on-premises, with centralised control and local availability. For edge and IoT scenarios, JFrog Connect supports remote management.
Why Communardo?

As an Atlassian Platinum Solution Partner and Specialised Partner for Software Development, we bring a deep understanding of the entire software delivery lifecycle:
- Toolchain architecture: We design the interaction between Jira, Bitbucket/GitLab, JFrog and other tools as an integrated platform
- Implementation: Setting up Artifactory, repository structures, access rights and pipeline integrations
- Migration: Transferring existing artefacts from Nexus, GitHub Packages or other repositories to JFrog
- Licence advice: Pro, Enterprise or Enterprise+? Cloud or self-hosted? We’ll find the right model
- Managed Services: Ongoing operation, monitoring and support for your JFrog instance
Who is JFrog + Atlassian relevant for?
Licensing & Procurement
JFrog offers various editions to suit different requirements:
Hosting options: JFrog Cloud (SaaS) | Self-hosted (AWS, StackIT, on-premises)
Communardo can provide you with expert advice on the best edition and team size – and a one-stop shop for procurement.
FAQ
Two completely different products: JFrog Xray is a security scanner for artefacts and dependencies, integrated into JFrog Artifactory. Xpand IT Xray is a test management tool that is natively integrated into Jira. Both can co-exist within the same toolchain.
Yes. JFrog Artifactory supports all common repository formats and offers migration tools for migrating from Sonatype Nexus. We can assist with planning and carrying out the migration.
Bitbucket Pipelines is a CI/CD tool – it builds and tests your code. JFrog Artifactory manages the results of these builds, i.e. artefacts. The two complement each other perfectly: Pipelines produce, Artifactory manages and distributes.
GitLab CI pushes build artefacts directly to Artifactory via the JFrog CLI or API. Build information is automatically displayed in Jira. The combination of GitLab CI, JFrog and Jira is a tried-and-tested enterprise pattern.
Yes. JFrog offers self-hosted options that can be run in completely isolated environments – which is relevant for the defence sector, critical infrastructure and strictly regulated industries.
Do you have any questions or would you like some advice from us?
Arrange a personal, no-obligation consultation with our Atlassian Sales Experts.

Your contact person
Your Atlassian Sales TeamWe're happy to help you
- Kleiststraße 10a, 01129 Dresden, Germany
- Tel: 0800 8 776 776
- sales@communardo.de